Cloud Security Posture Management: CSPM, CNAPP, CWPP, and WAAP Explained

It’s an alphabet soup in the cloud security market: Cloud security posture management (CSPM), CNAPP, CWPP, and WAAP. These cybersecurity product categories address different security requirements, from cloud configuration monitoring and compliance to workload and application protection. Discover how they differ, where they overlap, and how Atomicorp addresses important cloud security requirements. What Is Cloud […]
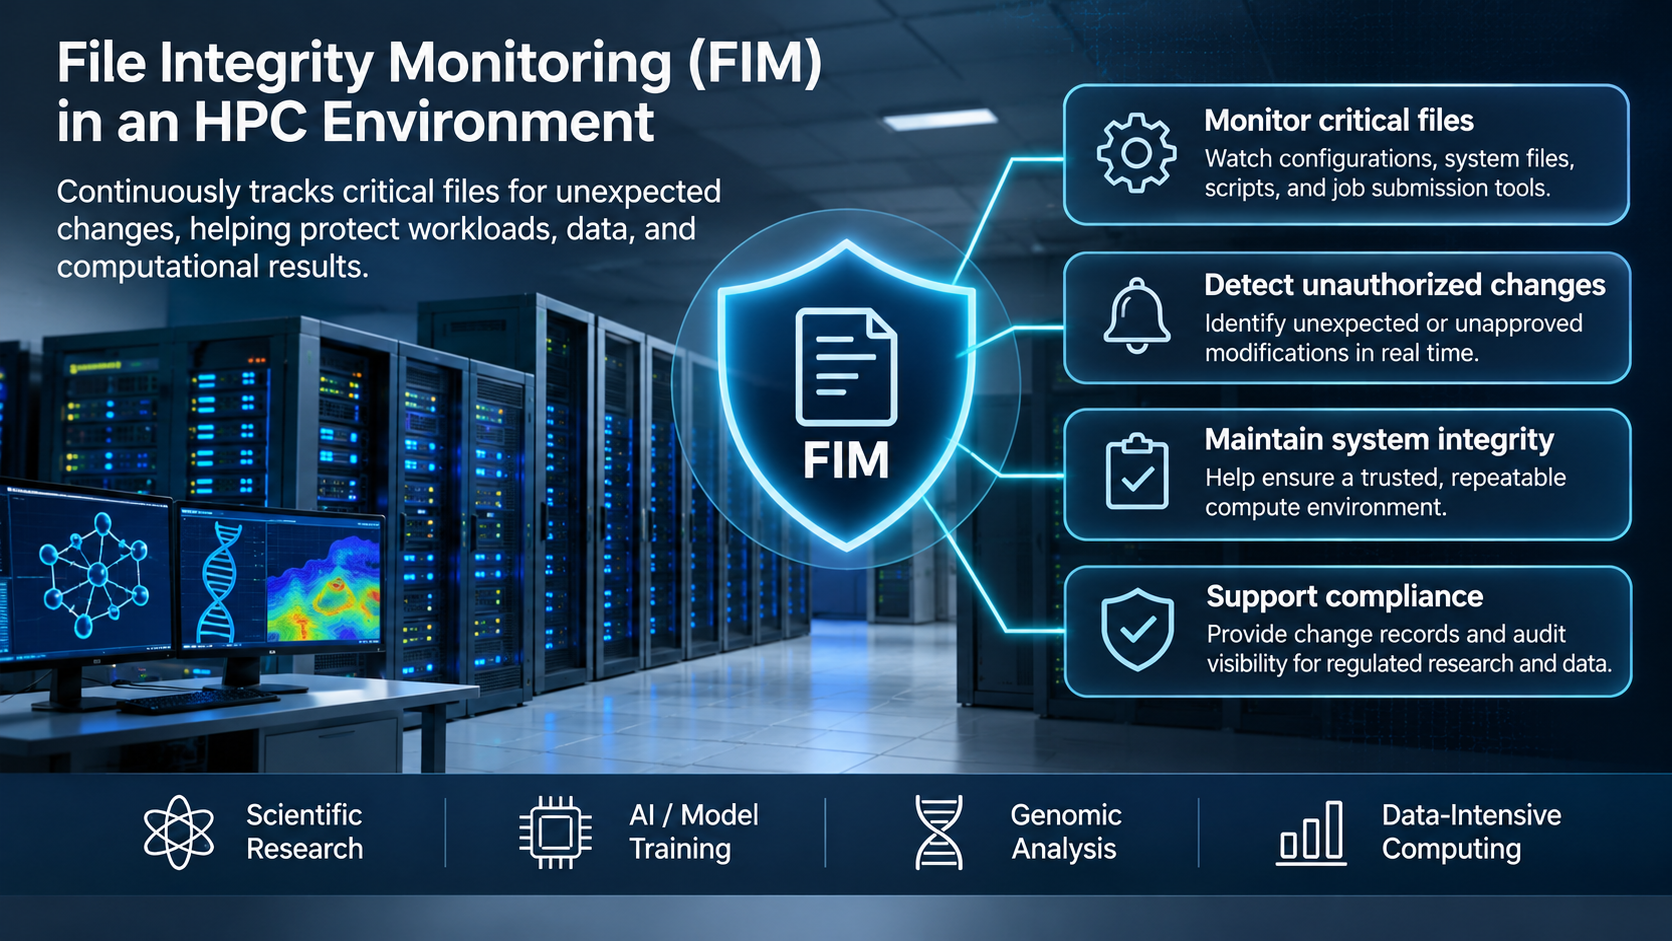
HPC Security Beyond OS Hardening: Protecting Enterprise Linux and Advanced Computing Infrastructure

High-performance computing (HPC) and AI infrastructure providers deliver the operating systems, management tools, and expertise behind demanding workloads. Yet their OS hardening and patching alone cannot address every cyber threat. Continuous file integrity monitoring (FIM), intrusion detection, vulnerability management, and automated response extend security across enterprise Linux and heterogeneous computing environments. For customers, these capabilities […]

Protecting Industrial Operations from Legacy IT Security Risks

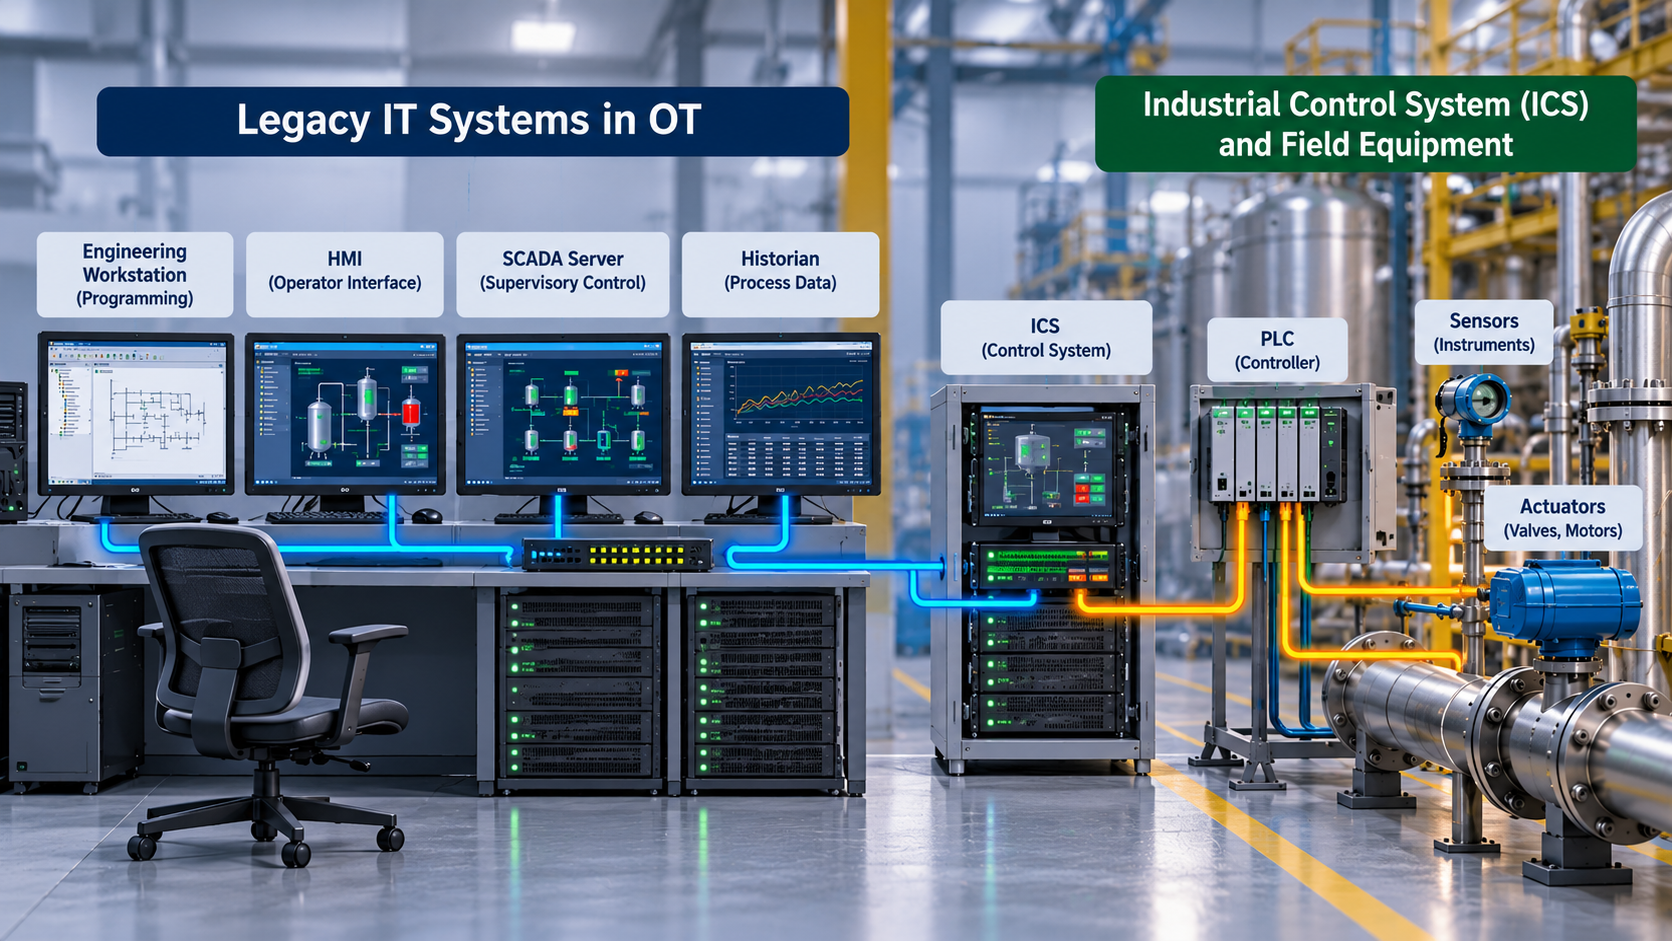
Legacy systems in OT environments often include aging Windows, Linux, and Unix-based computers that configure, monitor, and manage industrial equipment. These systems can introduce vulnerabilities into critical operations, while compatibility and uptime requirements complicate conventional security measures. Agentless EDR offers a way to extend continuous security and compliance monitoring to difficult-to-protect systems. Industrial operations rely […]

CVE Research Tools from Atomicorp

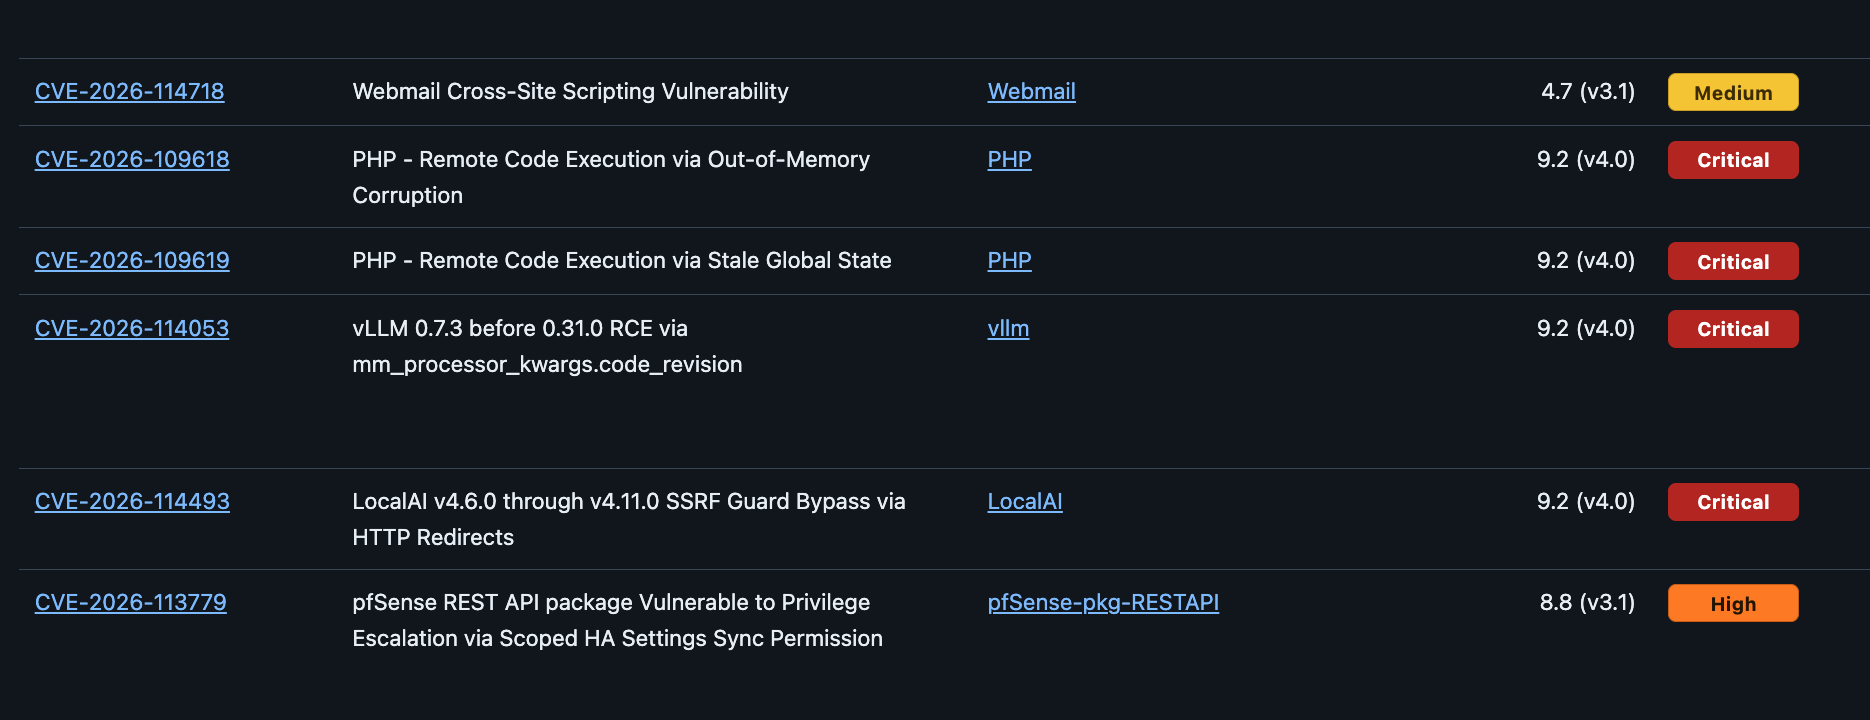
Atomicorp CVE Research Tools provide answers during uncertain times. A new CVE has been identified! How do you determine whether it affects your environment, whether a patch is available, and what protections may already stand between the vulnerability and an attacker? Atomicorp CVE Research Tools at research.atomicorp.com provide a place to investigate selected CVEs and […]

The WAF Blind Spot: What Basic Web Application Protection Can Miss

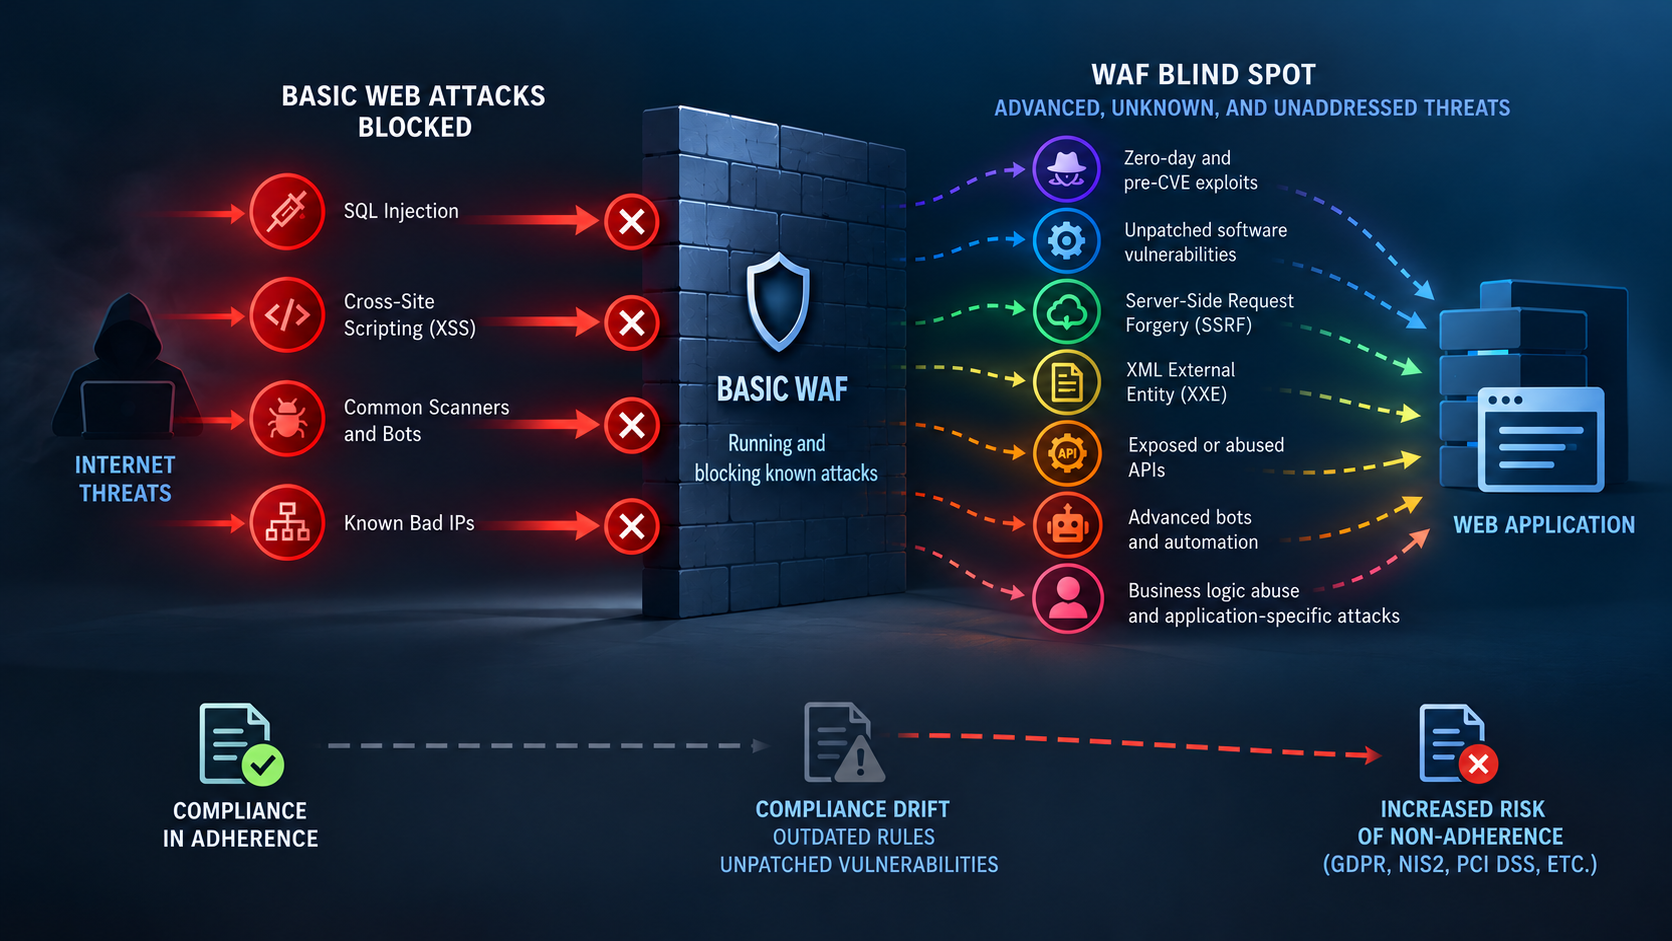
A WAF can be running, correctly configured, and blocking known attacks while still leaving significant gaps in application security. Limited inspection, outdated WAF rules, exposed APIs, and unpatched software vulnerabilities can create security gaps that attackers may exploit. For enterprises, CDN providers, and security integrators, effective web application protection requires more than baseline OWASP Top […]

SIEM Security Monitoring: Turn Security Data Into Action

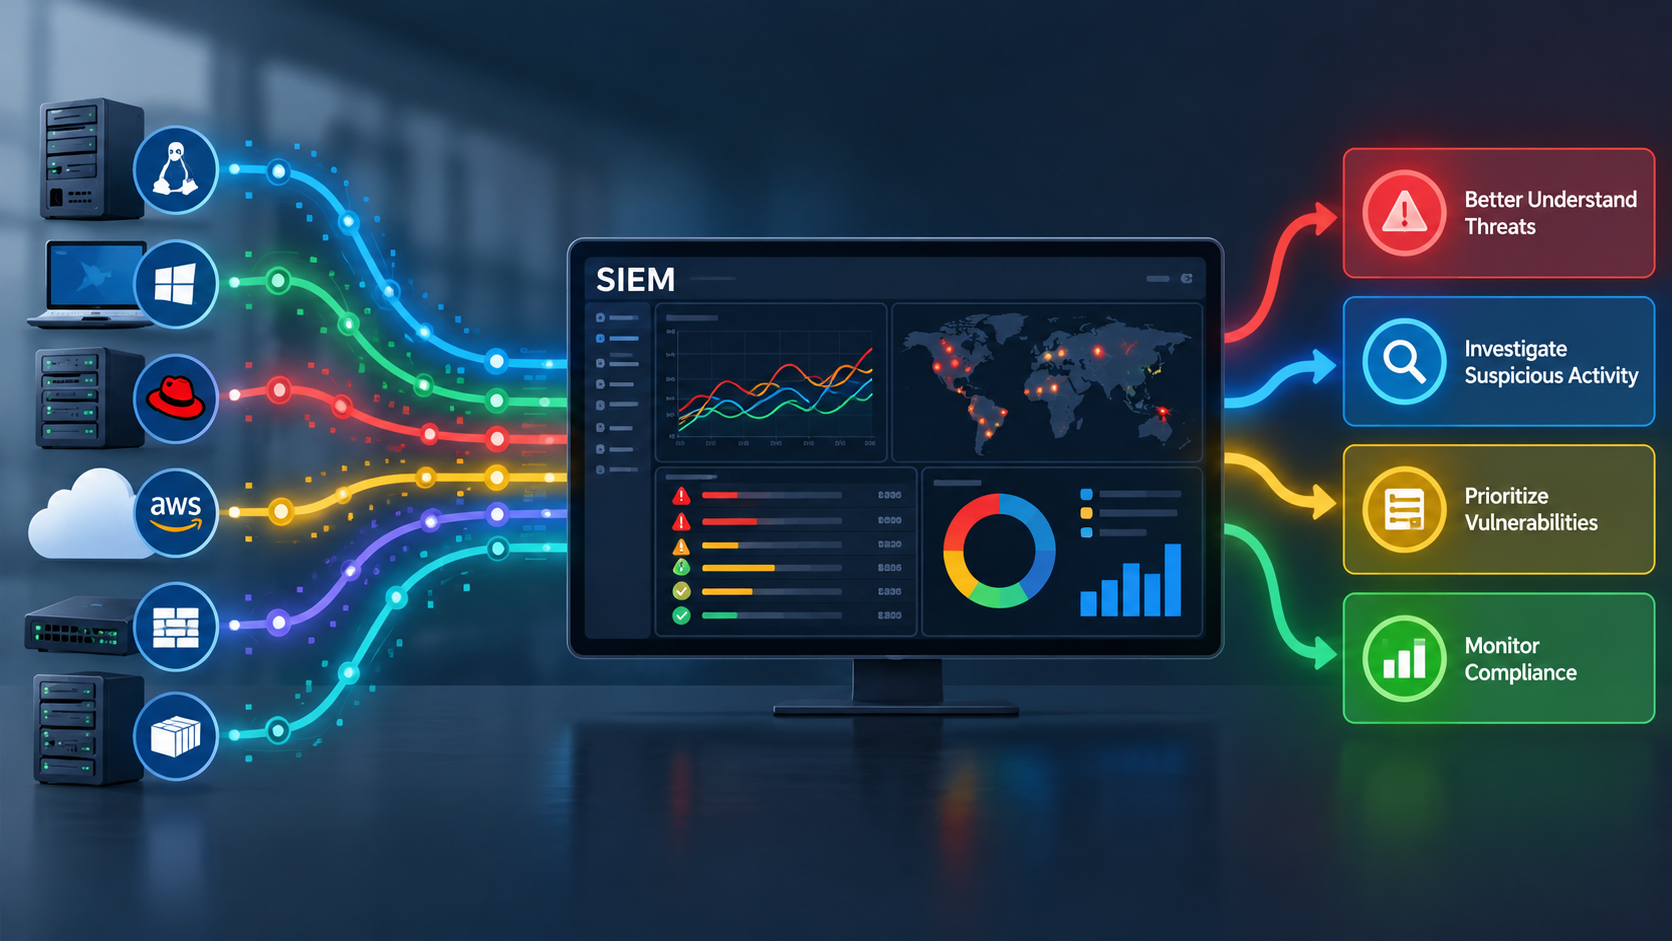
Leverage SIEM security monitoring in an endpoint detection and response (EDR) system that provides multi-SIEM and multiplatform flexibility. What Is SIEM Security Monitoring? Security information and event management (SIEM) brings security events, logs, and other telemetry together so organizations can detect threats, investigate activity, monitor compliance, and respond more effectively. Instead of viewing security activity […]

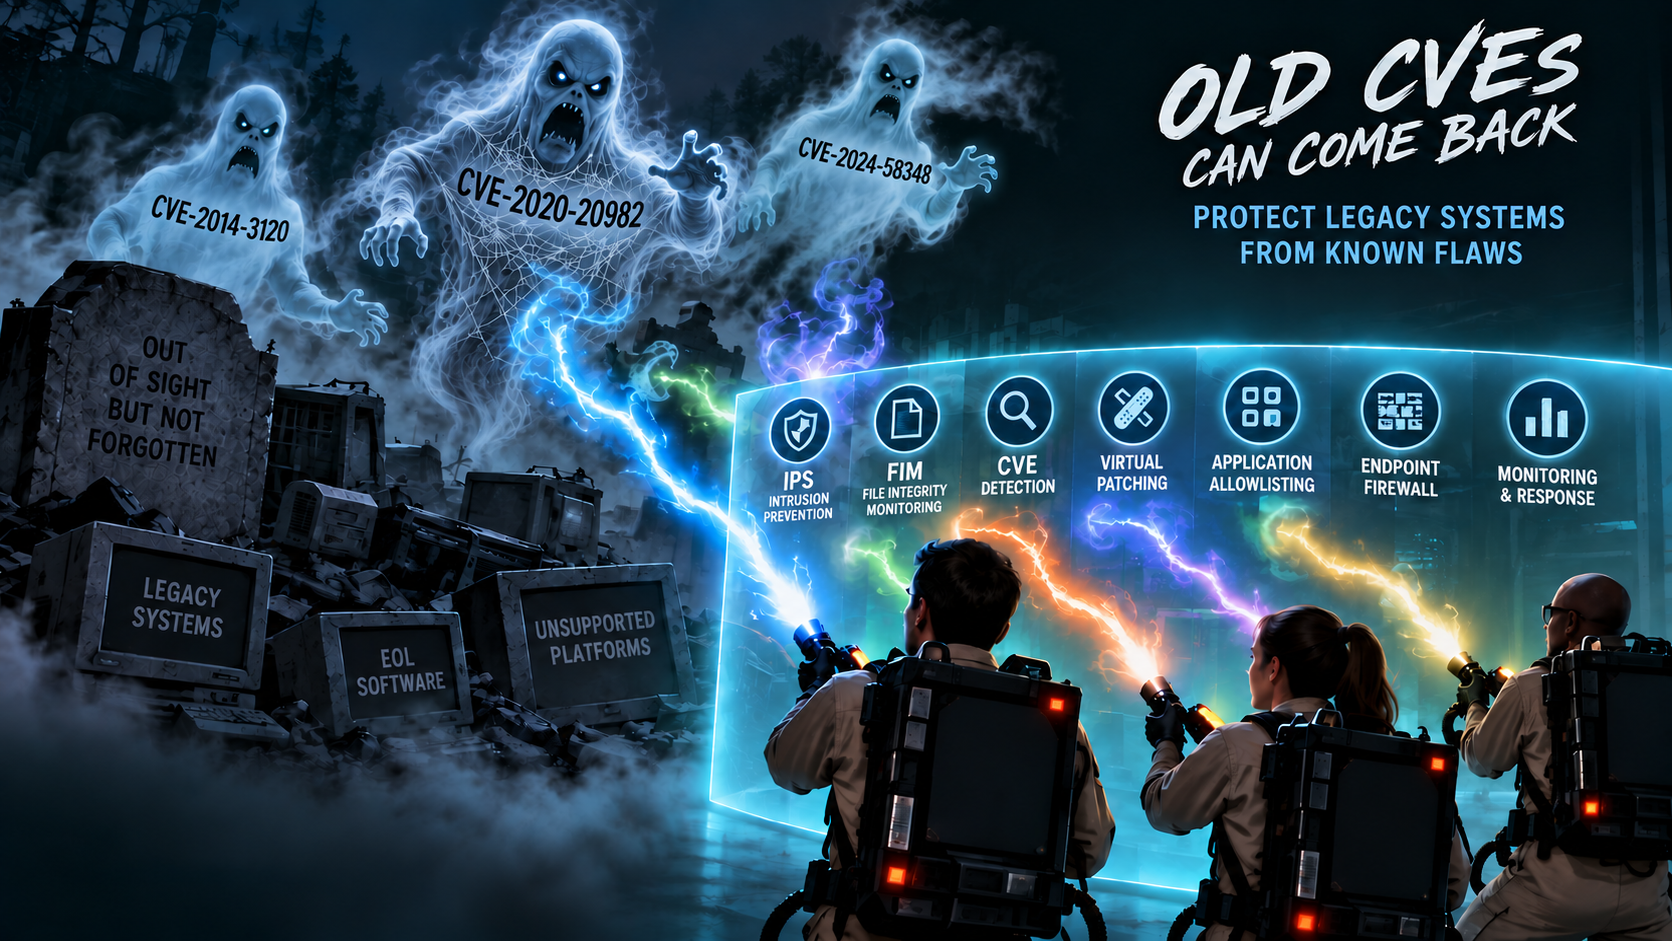
The Vulnerability Came Back: Why Old CVEs Still Demand Attention

Old vulnerabilities do not necessarily disappear from attackers’ playbooks. Instead, older CVEs can remain actively exploited years after their initial disclosure, particularly when vulnerable legacy and end-of-life (EOL) systems remain in operation. As artificial intelligence (AI) and automation accelerate vulnerability exploitation, organizations need to identify and protect weaknesses regardless of their age. Atomicorp helps organizations […]

Compensating Security Controls for When You Can’t Patch

Can’t Patch Old Software Vulnerabilities? Use Compensating Security Controls Unpatched software systems are an unfortunate reality for many organizations. When vulnerable IT and OT systems can’t be patched, compensating security controls and a defense-in-depth strategy help mitigate the risk while keeping critical systems running. Why Some IT and OT Systems Can’t Be Patched Patching known […]

The Endpoint Never Went Away: Why Host-Based Security Still Matters

Host-based security remains a critical layer of cybersecurity even as organizations shift infrastructure and security operations to the cloud. Servers, workstations, virtual machines, cloud instances, container hosts, legacy systems, and OT endpoints still run applications, process data, and deliver the programs defenders need to protect. Host-based security monitoring provides visibility into what is running, what […]